Governance that satisfies audits is not the same as governance that works
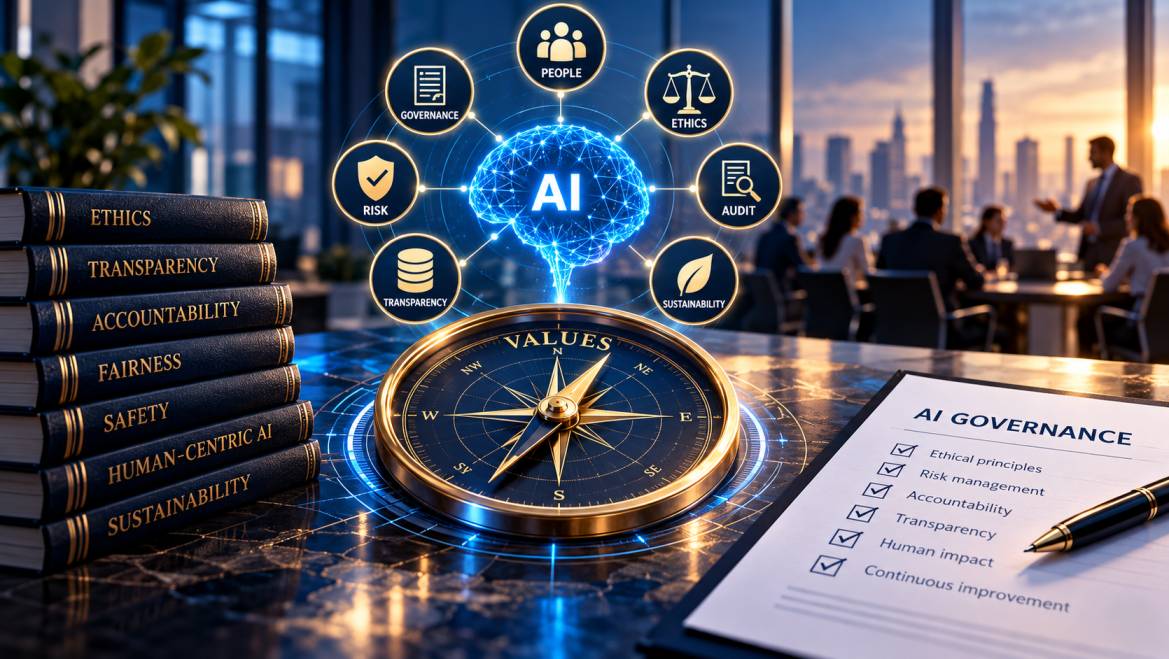
Ethical principles for AI are abundant; their translation into organisational practice is not. The paper argues that compliance-oriented governance, built around documentation and conformity checks, is valuable but structurally insufficient where AI shapes decisions about people’s access to credit, work, care or public services.
The reason is decoupling: formal structures that satisfy auditors while leaving consequential decisions unchanged. Drawing on institutional theory, business ethics research, stakeholder theory and the risk- and rights-based traditions of AI governance, the paper derives six design requirements and proposes the Ethical Governance Integration Model (EGIM). It maps the model to ISO/IEC 42001, illustrates it with a composite retail bank, and sets out implications for auditors, certification bodies and standard-setters.
The audit readiness paradox
Institutional theory distinguishes two ways formal governance drifts from practice. In policy–practice decoupling, policies are adopted but not implemented. In means–ends decoupling, they are implemented, but the activities they mandate are only loosely connected to the outcomes they exist to secure. Mature AI governance is most exposed to the second: every risk assessment can be completed and filed without any of them altering a design, delaying a deployment or changing how a system treats people.
The paper calls this the audit readiness paradox: the more completely governance is organised around demonstrable conformity, the easier it becomes to achieve conformity without achieving its purpose. This is not a claim that audits are futile. ISO/IEC 42001 already requires organisations to evaluate the effectiveness of their AI management system. The question is what counts as evidence of effectiveness.
Illustrative examples from the paper’s composite case.
Six design requirements
The paper translates each theoretical lens into a requirement that any governance model must meet if it is to resist decoupling.
Evidence of effect
Every mechanism must generate evidence that it changes decisions, not only that it exists.
Build on compliance
Values-driven mechanisms sit on, not instead of, the compliance infrastructure.
A voice for those affected
Give affected parties influence proportionate to risk, and record its effect.
Incentives and speaking up
Align incentives with commitments and protect those who raise concerns.
Non-negotiables
Combine risk-proportionate controls with explicit constraints that are not traded against benefits.
Beyond the firm
Extend governance to suppliers and make decisions reviewable.
The Ethical Governance Integration Model
The EGIM is a five-dimension framework for embedding ethical reasoning in an AI management system. It complements standards and regulation rather than replacing them, and it is not itself a certifiable standard. Its distinguishing feature is that every dimension is paired with effectiveness evidence: observable signs that the mechanism is changing decisions.
- Ethics Charter and non-negotiable uses
- Incentives aligned with commitments
- Use × population vulnerability tiers
- Triggered reclassification
- Ethics Board with authority to halt
- Participation with recorded response
- Impact assessment and named owners
- Reviewable records and redress
- Scheduled and event-triggered review
- Protected concern-raising
Ethical Policy Anchoring
Establish what the organisation will and will not do with AI, in terms that bind future decisions.
An Ethics Charter naming values and non-negotiable uses, developed with stakeholder input; sponsor incentives aligned with its commitments.
Use cases declined, narrowed or delayed because of the Charter.
Risk-Proportionate Controls
Calibrate controls to the risk each system poses to the people it affects.
Tiers set by intended use and by the vulnerability of the affected population; justified fairness metrics; reclassification triggered by retraining, drift or supplier changes.
Reclassifications that followed triggers; group-level results that led to action.
Stakeholder Inclusion Mechanisms
Give affected parties structured influence over systems that affect them.
An Ethics Board with defined authority to delay or halt deployments; proportionate external participation with recorded responses.
Deployments conditioned or stopped; stakeholder input traceable to changes.
Transparent Accountability Structures
Make someone answerable for each system’s impacts, and give individuals recourse.
Impact assessment; named owners, including for supplier components; reviewable records; accessible redress.
Designs changed by assessments; remedies granted; decisions reconstructable on sampling.
Continuous Ethical Review Cycles
Keep governance current as systems, contexts and expectations change.
Scheduled and event-triggered review; protected channels for raising concerns; findings fed to management review.
Reviews triggered by events, not only the audit calendar; concerns raised and resolved.
Working inside ISO/IEC 42001
The EGIM operates inside an ISO/IEC 42001 management system rather than alongside it. The full paper includes an indicative clause-by-clause mapping and relates the model to the companion standards ISO/IEC 42005 and 42006. Its practical consequence is a sharper test of effectiveness: sample decisions, not only documents. That test applies differently to each assurance role.
Internal audit
Has the most freedom. It can adopt EGIM criteria, triangulate documents against decision records and interviews, and report divergence between them as a finding.
Certification bodies
Audit against the standard’s requirements and cannot require mechanisms it does not. They can probe effectiveness more deeply within those requirements, supported by the competence requirements of ISO/IEC 42006.
Assurance beyond certification
Ethics-based audits and end-to-end algorithmic audits can adopt the EGIM’s criteria directly.
What an EGIM assessment adds
The paper applies the model to Horizon Bank, a composite mid-sized retail bank preparing for ISO/IEC 42001 certification, whose documentation an internal review has judged sufficient. An EGIM assessment separates its gaps into two groups.
Would be nonconformities if detected
A high-risk credit model retrained twice without reassessment, despite an internal flag on residual fairness risk.
Satisfy the standard, change nothing
A governance committee that has never conditioned or halted a deployment. A policy that has never constrained a decision.
The second group is where the model adds most. The paper also sets out a sequenced response: close the high-stakes control gaps first, then give governance bodies real decision rights, and only then write the Ethics Charter. Mechanisms come first; the documents that codify them follow.
What it means for…
Organisational leaders
Treat ISO/IEC 42001 conformity as a foundation, not an end point.
Auditors
Sample decisions as well as documents.
Standard-setters
Articulate what evidence of effective AI governance looks like, especially for stakeholder engagement and impact assessment.
Regulators
Reward substantive governance, so that certification is treated as one indicator of good governance, not proof of it.
This is a conceptual paper. The EGIM has been designed and demonstrated, not yet empirically validated; the bank is a constructed composite, not a case study; and the model was developed from a practitioner perspective in AI governance and audit. The paper sets out an agenda for testing it, and also covers proportionality for smaller organisations, applicability across EU, UK and GCC contexts, and the pressures that generative and agentic AI place on system-by-system governance.
Request the full paper
The full paper, with its figures, tables and 54 references, is available free on request. Tell us where to send it.
Miheisi, Y. (2026). Beyond compliance: Towards a values-driven framework for AI governance in high-stakes organisational environments [Working paper]. Enterprise Intelligence Center.